Swissbitブログ
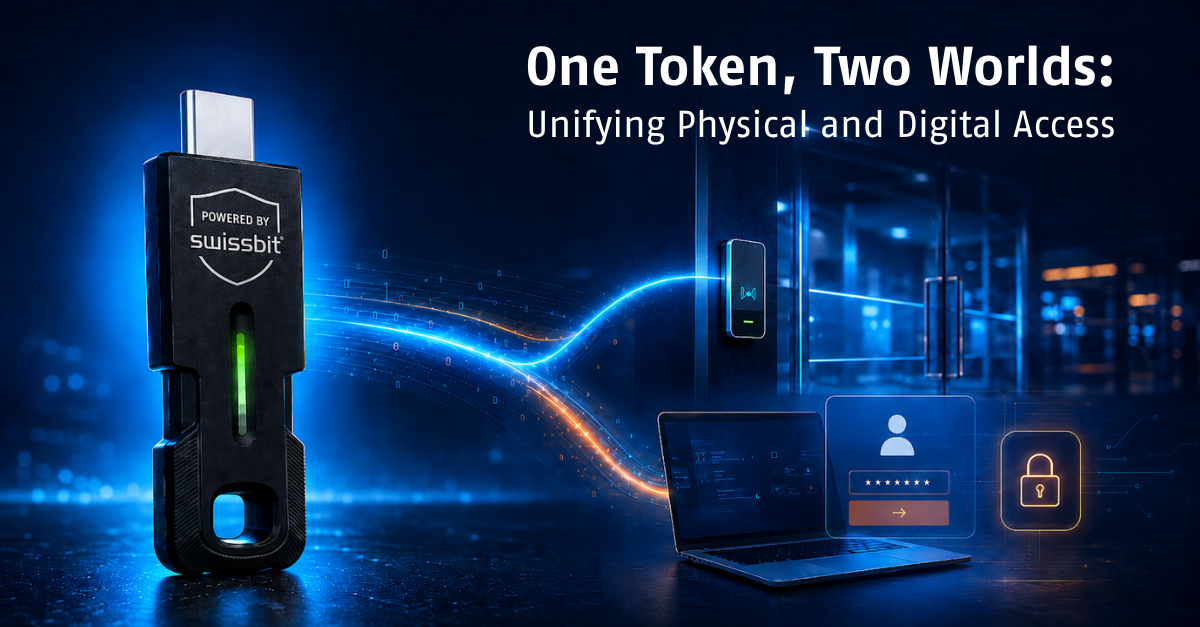

One Token, Zero Gaps: Physical and Digital Access Control
Physical and digital access are two sides of the same security challenge. Discover how the Swissbit iShield Key 2 combines phishing-resistant FIDO2 authentication with secure physical access, helping organizations reduce complexity, close security gaps and strengthen Zero Trust.
Hardware Authentication in Manufacturing: Why FIDO2 Keys Are the Future of Industrial Security
In my latest blog post, I examine the challenges facing the manufacturing industry more closely. What solutions are available, and what benefits do they offer? Finally, I share my conclusion.
Identity attacks in the financial sector: Why strong, hardware-based authentication is now essential
In my latest blog post, I take a closer look at the financial sector. What challenges does the industry face? What solutions exist, and what are their benefits? Finally, I share my conclusion.
Physical and logical access control in one security key
Physical and logical access control often run on separate systems: one badge for the door, another method for the login. In this post, I explain why it pays off to look at both together. First, I will explain the difference, and then I will discuss the advantages of such a combined solution for companies. Finally, I present the solution that Swissbit offers.
AiTM attacks: How attackers bypass MFA and how to stop them
In my new article, I examine Adversary-in-the-Middle (AitM) attacks and compares this novel approach to traditional Man-in-the-Middle (MitM) attacks. The article shows how multi-factor authentication (MFA) can be bypassed as a core feature, but there is an effective way to prevent this: FIDO2
EU Regulation DORA: How hardware authentication can secure financial companies
The Digital Operational Resilience Act (DORA) is the next major EU regulation to come into force. The aim of the EU regulation is to strengthen the IT security of European financial companies. Hardware authentication via FIDO Security Key can help effectively, as this article by Travis Dunn shows.
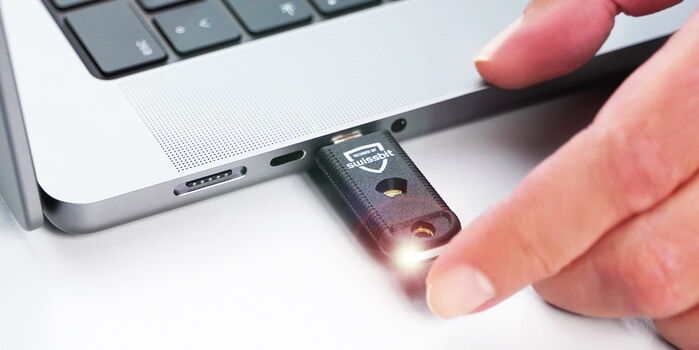
認証の基礎:MFAにハードウェアトークンを使用する7つのメリット
「認証の基礎」シリーズの最新ブログ記事では多要素認証(MFA)の基本を解説し、さらに、ハードウェアトークンが他の認証方法よりも優れたセキュリティや使いやすさを実現する仕組みとその理由を説明します。この物理的な認証デバイスが、フィッシングやその他のサイバー脅威に対するオンライン保護機能として最適な理由をご確認ください。
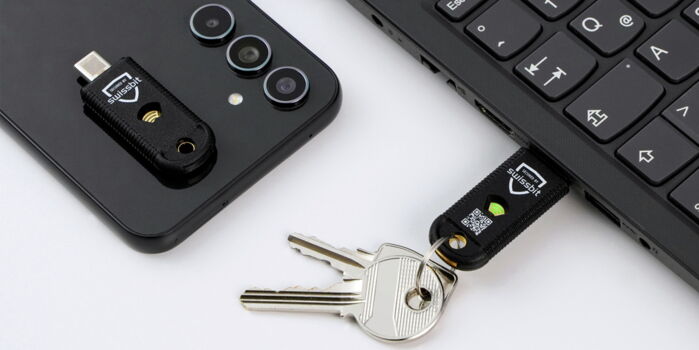
認証101:iShield Keyシリーズの5つのメリット
「認証101」シリーズの初回となる本ブログ記事では、iShield Keyシリーズがウェブサイト、アプリケーション、オンラインサービス、企業ネットワークで認証機能を果たすことによって、どのようにユーザーのデジタルIDを保護するか、その方法と理由について説明します。
EU Regulation NIS2: Don't Get Caught Off Guard!
The EU's NIS2 Directive is tightening cybersecurity for critical infrastructures. Navigating these regulations can be daunting. Alexander Summerer explains what NIS2 means for your organization and how Multi-Factor Authentication (MFA) can help you comply. Discover who is affected, the penalties for non-compliance, and why USB tokens might be the most secure and cost-effective MFA solution.
認証の基礎:FIDO2の紹介
今回から、認証、アイデンティティとアクセス管理、サイバーセキュリティの基礎をテーマとして、スイスビットのIAMテクノロジストが解説する新しいブログシリーズを始めます。この最初の投稿では、FIDO2標準の基礎を説明し、この強固なセキュリティプロトコルの実装を目指すソフトウェア管理者にとって重要な情報と実用的なヒントを紹介します。
MFA is essential: Why a hardware token can make all the difference
At the beginning of June, the Christian Democratic Union (CDU) in Germany was the victim of a serious cyberattack. Hackers exploited a VPN vulnerability and accessed sensitive data. This attack underlines (once again) the urgent need for multi-factor authentication (MFA), says Claus Gründel, General Manager for Swissbit's security solutions, and emphasizes the importance of decisive action in cyber security.
Unlocking the Future of Cybersecurity: Zero Trust Solutions with Hardware Authentication
Dive into the concept of 'zero trust' and learn practical implementation strategies to safeguard your company's critical resources and data against internal and external threats. In his blog post – and our corresponding white paper – Alexander Summerer reveals how zero trust principles, including hardware-based authentication like FIDO security keys, can elevate your security measures and proactively minimize risks.
認証101:よく知られている5つの認証方法の比較
「認証101」シリーズの2回目は、デジタルIDを認証・保護する方法を紹介します。まず、各認証方法の長所と短所がどこにあるかを紹介し、最後にそれぞれの簡単な評価を示します。まとめの項では、iShield Keyシリーズについても触れています。